Where ProofRelay Sits
Between the decision and the action
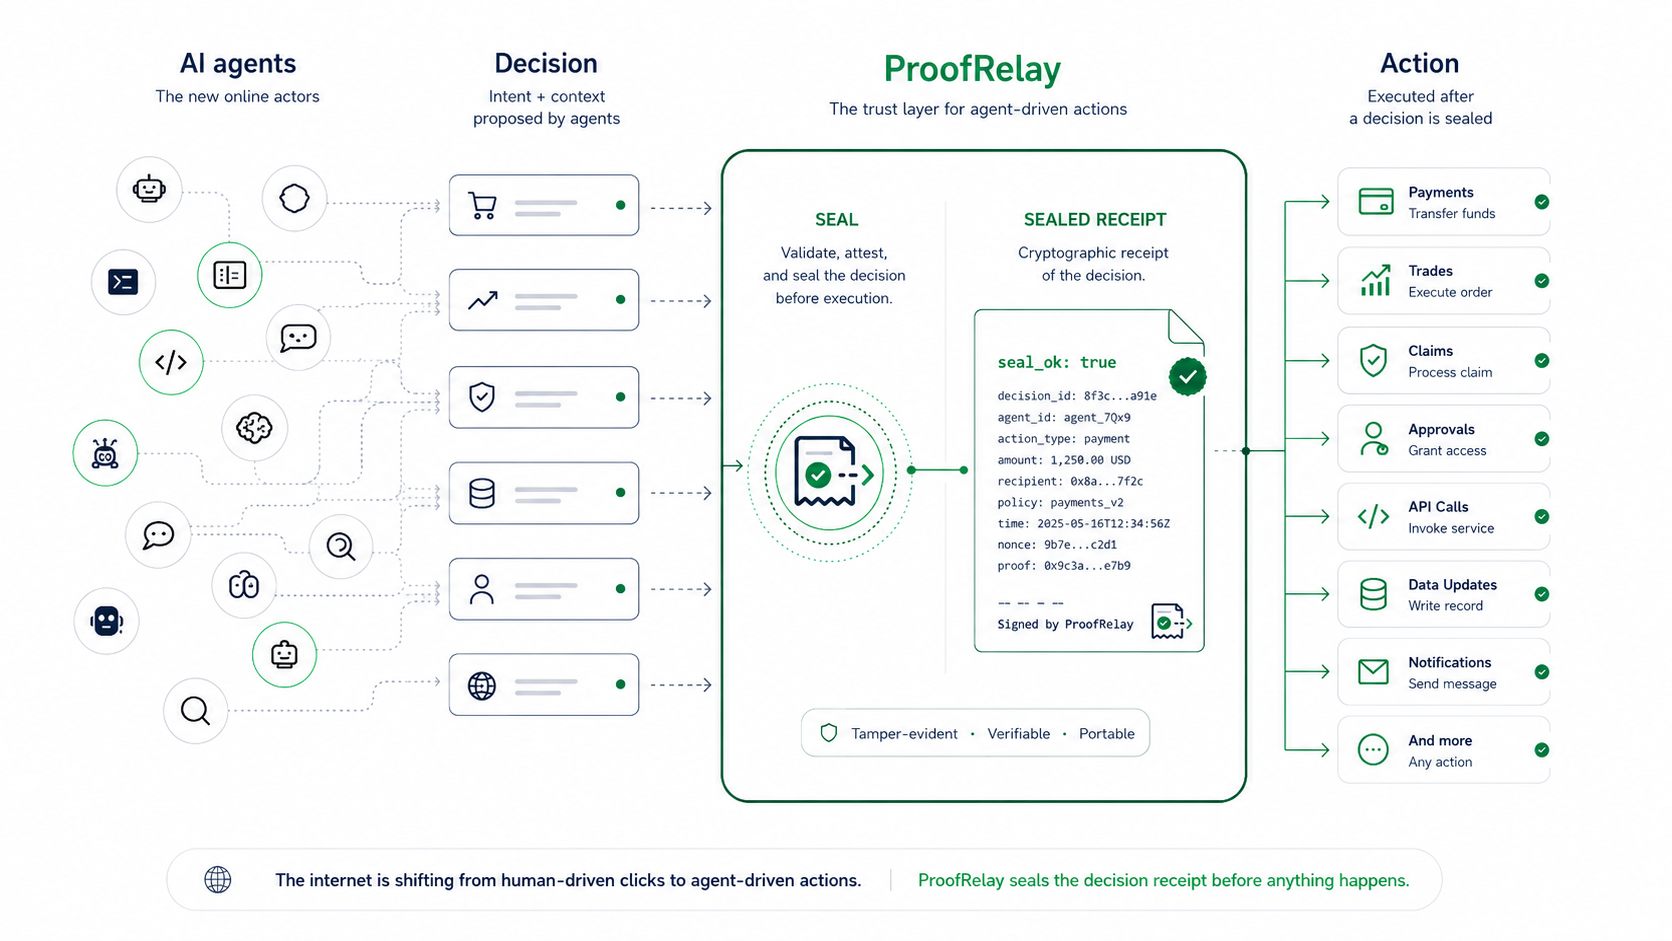
Enter your ProofRelay API key to continue to Stripe checkout.
Redirects to Stripe's secure checkout. No charge until you confirm.
ProofRelay seals an agent's inputs, policy, and reasoning before it acts. Provably untampered, not just logged. Verify a real receipt right now:
POST your agent's decision (inputs snapshot, ruleset, and reasoning trace) to /api/execute/decision. Attach your API key. ProofRelay seals it before anything executes.
ProofRelay hashes your payload with a server-side secret, timestamps it, and stores the receipt. Alter any stored field and the recomputed seal no longer matches. Your response includes a receipt ID and the seal value.
At any point, seconds or years later, call /api/verify/decision?id= with the receipt ID. ProofRelay recomputes the seal from stored fields rather than returning a stored flag. Any field alteration produces a mismatch. No API key required. Any counterparty can verify independently.
Your auditors, regulators, or counterparties now have cryptographic proof of why the decision was made. Not reconstructed from logs. Sealed before execution.
Still figuring out where ProofRelay fits? These scenarios show exactly what gets sealed, who verifies it, and what it proves across four industries where AI agents are already making consequential decisions.
Inputs snapshot, policy ruleset, policy condition evaluation results, and reasoning trace are sealed as a single indivisible unit using HMAC-SHA-256. Modification of any field breaks the seal on recomputation.
ISO 8601 timestamps are embedded in the hash itself, not a metadata field. You cannot backdate or forward-date a receipt without detection.
Built for autonomous decision loops. Your agent seals the inputs, policy, and reasoning before acting, not after. Downstream agents and auditors see what the agent saw, what policy governed it, and what reasoning produced the decision.
POST to execute. GET to verify. No SDK required, no complex setup. Works with any HTTP client in any language. Production-ready in minutes.
Subscribe, and your API key arrives in seconds via automated email. No waiting, no sales calls, no approval queues. Start sealing actions immediately.
Every receipt is publicly verifiable by any party using only the receipt ID. Verification recomputes the seal from stored fields rather than reading a stored flag, so tampering is detectable even if the database is compromised.
Authenticated requests pass your API key in the x-api-key header. Your key is issued automatically when you subscribe and emailed to you instantly.
Keys are prefixed pr_live_ for production. Keep your key secret. Treat it like a password. You can rotate it from the customer portal.
Call POST /api/execute/decision to seal a decision before it executes. Pass your agent ID, decision, ruleset, inputs snapshot, and reasoning trace. The response includes a receipt_id, the seal, and a public verification URL. Store the receipt ID.
Use the requests library or any HTTP client. The API is pure REST. No SDK required.
Call GET /api/verify/decision?id= with your receipt ID. No API key required. Any counterparty can run this independently. A response with seal_ok: true is your cryptographic proof the decision was untampered.
Simple GET request. No API key required. Pass the receipt_id you stored at execute time.
Execute returns a 201 Created. Verify returns a 200 OK. All responses are JSON.
The three-timestamp structure (inputs_captured_at, decision_made_at, and receipt_sealed_at) provides a cryptographically attested decision lifecycle sequence. Any verifier can confirm the temporal relationship between input capture, decision formation, and sealing.
ProofRelay returns standard HTTP status codes with a JSON error body containing a code and message field.
A real sealed receipt, one click away. No account, no API key, no operator trust required. When you're ready to seal your own decisions, the free tier includes 50 receipts a month with no card required.